Cookie Consent Banner & Privacy Compliance (GDPR/CCPA)
📁 Compliance & Billing
🕐 Updated 54 minutes ago
Cookie Consent Banner & Privacy Compliance (GDPR/CCPA)
Ensure your web push notifications adhere to international privacy framework requirements, including EU GDPR, California CCPA/CPRA, and the ePrivacy Directive.
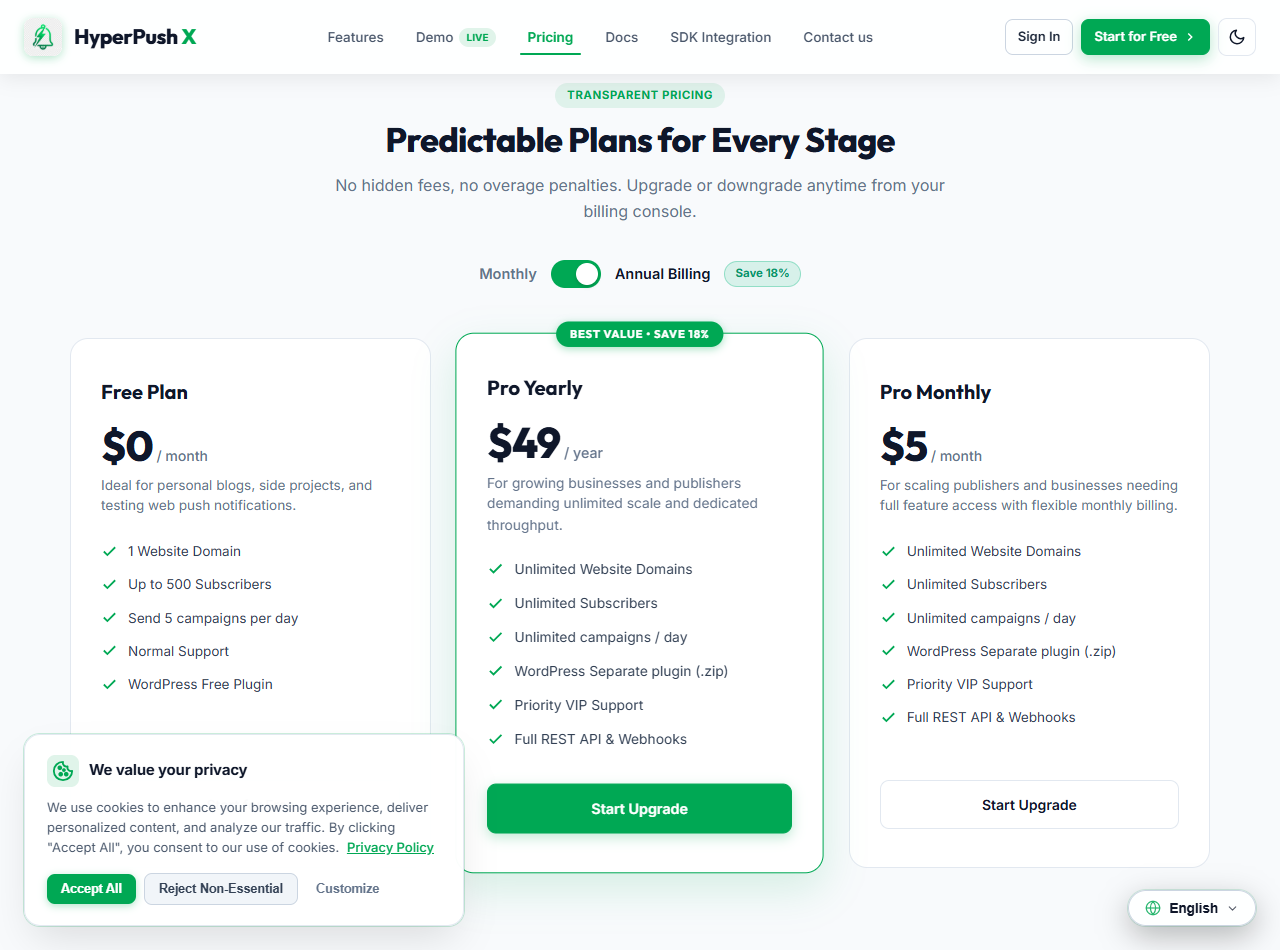
📷 Live System Interface: Landing Page Privacy Banner
📐 Cookie Consent Banner Layout & Rules
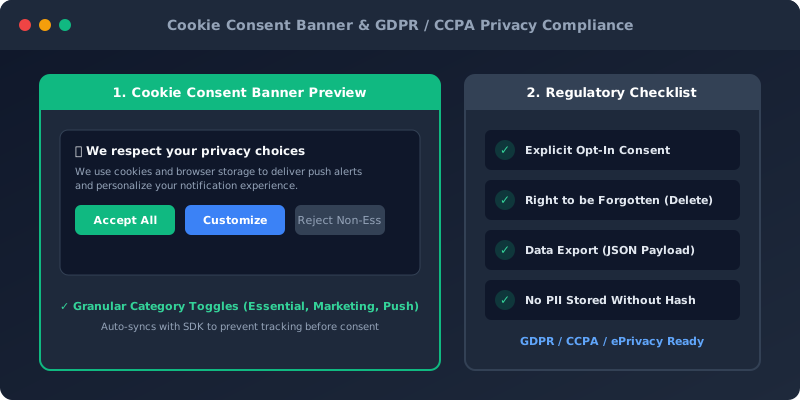
🛡️ Privacy Compliance Checklist
HyperPush X is architected from the ground up to respect user privacy and adhere to global compliance standards:
- Explicit Opt-In Consent: Push notification permission prompts are never triggered automatically without explicit visitor interaction or clear soft prompt confirmation.
- Zero Personally Identifiable Information (PII): HyperPush X stores anonymous VAPID browser push endpoints. We do not store names, email addresses, IP addresses, or personal credentials unless explicitly provided by your web application.
- One-Click Unsubscribe: Subscribers can revoke push permissions directly from their browser settings at any time with a single click.
- Right to Be Forgotten (Data Purging): Effortlessly purge subscriber tokens and historical logs upon request from the HyperPush X Web Console or WordPress Plugin settings.
🍪 Cookie Consent Banner Integration
If your website utilizes a Cookie Consent Banner (e.g. CookieBot, OneTrust, or custom modal), follow these rules for seamless integration:
- Soft Prompt Delay: Set your HyperPush X soft prompt delay to trigger after the visitor accepts your website's cookie/privacy notice.
- Category Classification: Classify HyperPush X Service Worker push scripts under Functional / Communication Cookies in your CMP (Consent Management Platform).
- Zero Pre-Consent Registration: HyperPush X guarantees no Service Worker token registration occurs prior to visitor consent.
 HyperPush X Docs